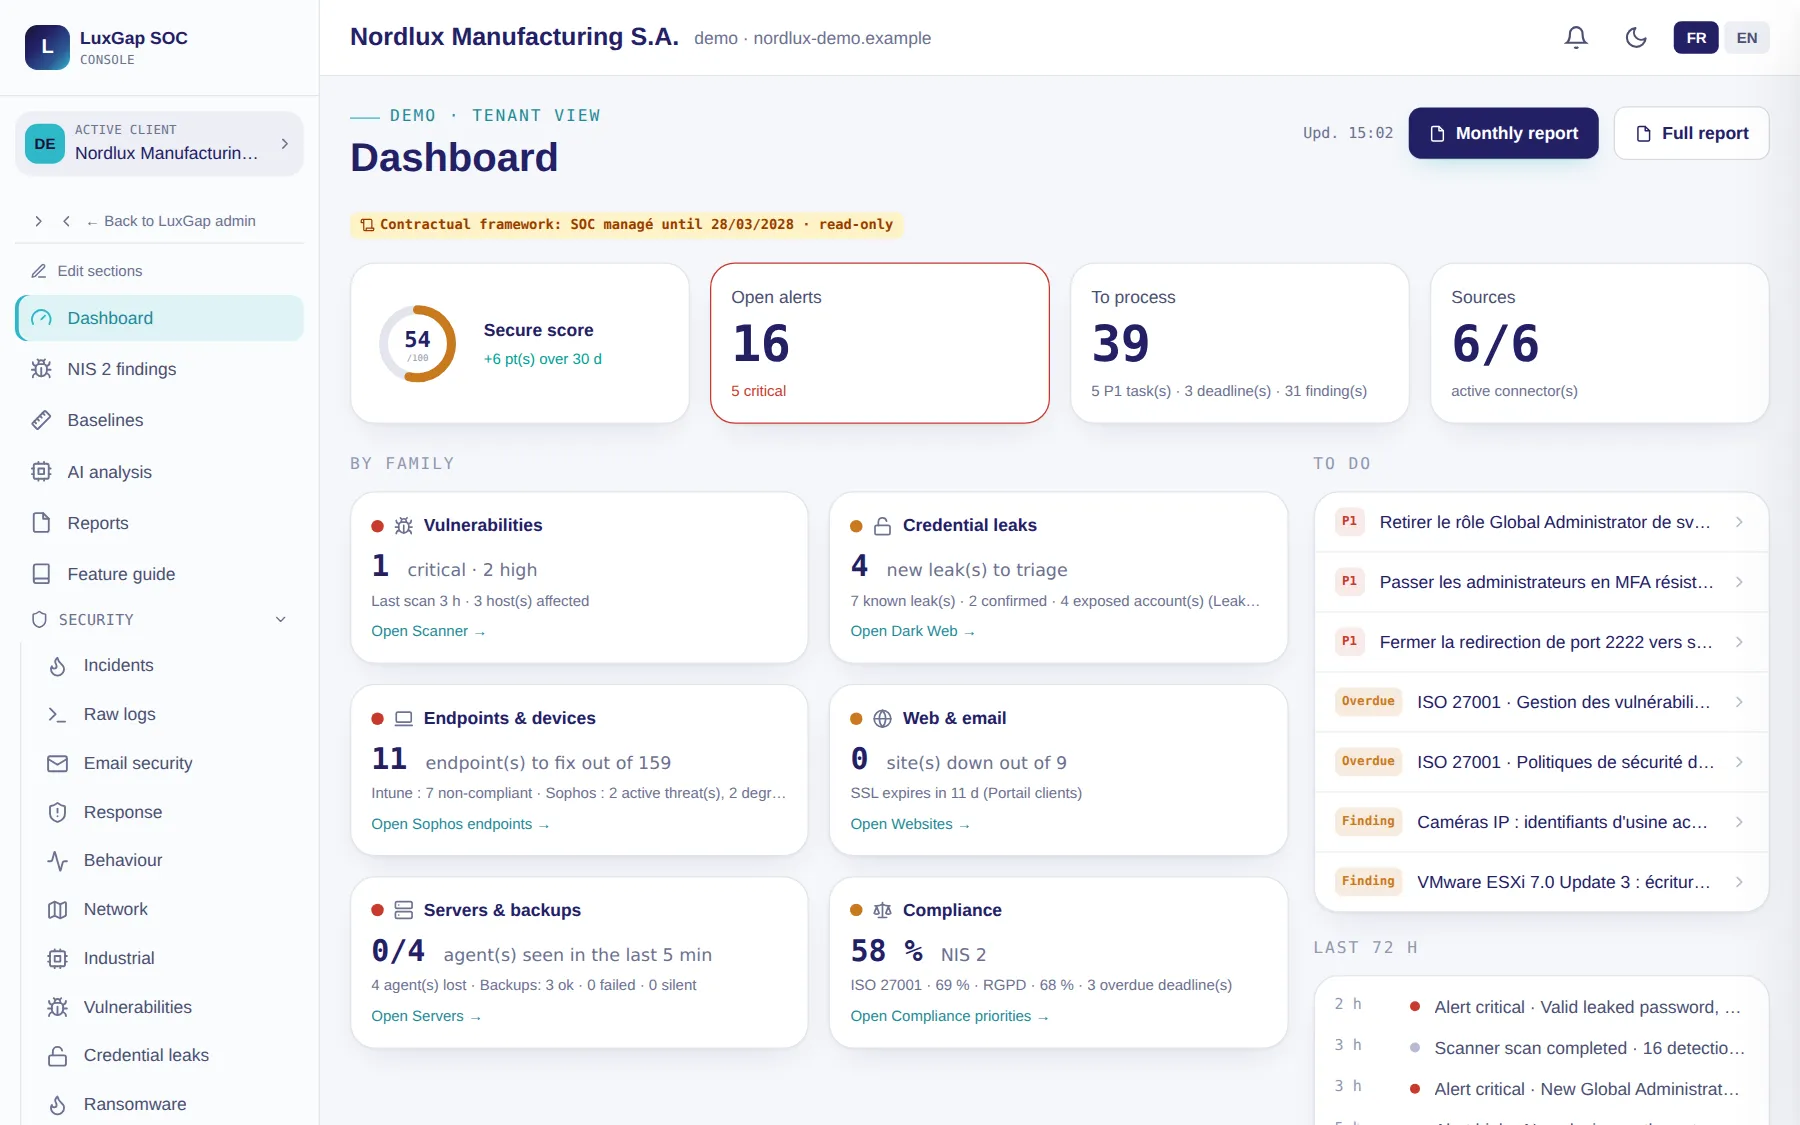
Nine features, one console, one team. Every feature feeds the IT task board and the coverage score.
Log collection and correlation
A sovereign SIEM/XDR that sees your entire perimeter
Logs from your Windows and Linux servers, firewalls and network equipment, applications, databases and cloud tenants are continuously collected, normalised and correlated. Detection rules are maintained by the LuxGap team and refined with every incident handled.
- Agents on servers, API connectors for the cloud, network log ingestion
- Cross-source correlation: a suspicious sign-in plus external sharing plus a mass download = one alert, not three
- Log retention in the European Union for your audits and investigations
- Detection rules updated with every incident the team handles
See it in pictures →
Correlation — 3 events from 2 sources → critical alert — account finance-02
Continuous cloud configuration audit
Microsoft 365 and Google Workspace, checked continuously
Multi-factor authentication, external sharing, automatic email forwarding, authorised applications, logging, data loss prevention, anti-phishing: every setting is checked continuously and every deviation becomes a hardening task. The platform automatically adapts to new features released by Microsoft and Google.
- MFA, sharing, forwarding, application, logging, DLP and anti-phishing controls
- Least-privilege connection, with the exact list provided before access is granted
- Detection of configuration changes between two checks
- Automatic adaptation to new Microsoft and Google features
See it in pictures →
Microsoft 365 configuration: 38 compliant controls · 4 deviations
External auto-forwarding allowed — 2 mailboxes
Your credentials, devices, executives and brand, monitored
Thirteen threat intelligence sources are queried for your domains: your employees' credentials sold on criminal marketplaces, devices infected by a credential stealer, database leaks, lookalike domains ready for phishing. Ransomware group leak sites are also read, and a watchlist tracks your executives, your IP addresses and your brands.
- Exposed accounts checked as often as every hour, with an alert as soon as one is detected
- Devices infected by a credential stealer, tracked until they are dealt with
- Validity of each leaked credential: probably still valid or changed since, without ever trying a password
- Lookalike and homograph domains spotted, flagged as soon as they receive mail or a certificate
- Targeted watch of your executives, your IP addresses and your brands
- Monitoring of ransomware groups' leak sites, for you and for your suppliers
See it in pictures →
Critical — 2 primary-domain credentials for sale — reset requested
Your antivirus alerts, finally read, correlated and acted on
Your endpoint protection solutions (ESET, Microsoft Defender and others) send their malware and suspicious behaviour alerts to the console. The team triages them, correlates them with the rest of the perimeter and initiates containment with you.
- Integration of your existing EDR, with no change of tool
- Correlation across endpoint, identity, cloud and network
- Unprotected or out-of-date endpoints identified and added to the task board
- Containment with your teams or your IT provider
See it in pictures →
Major — Suspicious behaviour blocked by EDR — endpoint compta-07 — triage in progress
Vulnerabilities and penetration testing
Find the weaknesses before they are exploited
Connected infrastructure is scanned regularly for known vulnerabilities; LuxGap experts carry out penetration tests on your applications and infrastructure. Every weakness becomes a prioritised task on the IT task board, tracked until it is fixed.
- Recurring vulnerability scans across the connected perimeter
- Penetration testing by LuxGap experts, for applications and infrastructure
- Prioritisation by criticality and actual exposure
- Remediation tracked through to closure, with evidence
See it in pictures →
Critical — Exploitable vulnerability exposed to the internet — srv-erp-01 — patch available
Connected devices, industrial systems and buildings
What other SOCs refuse to monitor
Sensors, locks and badges, cameras, lighting, server room air conditioning, UPS units, PLCs and industrial equipment: anything that emits a signal is connected, through building and industrial protocols or by passive network monitoring. Some control functions are available from the console, such as lighting or switching off a piece of equipment.
- Connection of the building's connected devices (for example via a Zigbee antenna) and technical equipment
- Passive monitoring of industrial networks, without disrupting production
- Physical and digital alerts in the same console: door opened out of hours, abnormal temperature, reprogrammed PLC
- Control functions from the console for equipment that supports them
See it in pictures →
Info — Server room: 31°C, threshold 27°C — air conditioning checkedSwitch on emergency lighting
Incident detection and response
Detect from the first hour, notify within the deadlines
Every alert is triaged by an analyst. When an incident occurs, the team contains it with you, prepares and submits the regulatory notifications to the CNPD, the ILR or the CSSF within the deadlines, documents the incident and updates the task board to prevent it from happening again.
- First-hour detection
- Containment with your teams or your IT provider
- Regulatory notifications drafted by our legal experts and submitted within NIS2, DORA and GDPR deadlines
- Full documentation and lessons learned
See it in pictures →
Detected 09:12 · Triaged 09:40 · Contained 10:05 · CNPD notified D+1 · Closed D+3
IT task board and coverage score
See what has been hardened, what remains to be done and in what order
Every deviation detected, every control to harden and every vulnerability feeds a task board shared with your team or your IT provider. The coverage score rises with every task closed and gives management a single, continuously updated figure.
- Controls to harden, detected deviations and priorities in one place
- Coverage score updated continuously
- Shared with your IT provider, without giving them access to anything else
- Full history for your auditors
See it in pictures →
Coverage score 91% · 14 open tasks · next: enable MFA on 3 service accounts
Console, reports and auditor access
A secure console for you, your CISO and your auditor
The monitoring console is available in French and English, with one account per user and mandatory MFA: email address, password and a one-time code. It is where you follow alerts, assets, tasks, incidents and reports; your auditor or external CISO has their own access.
- Mandatory MFA, TLS 1.3 encryption, one named account per user
- Activity reports and exportable evidence for your audits
- Dedicated read-only access for your auditor, DPO or CISO
- Feature requests sent straight from the console, with an assistant that helps you write them
See it in pictures →
LuxGap Safety — Monitoring consoleMFA REQUIRED